
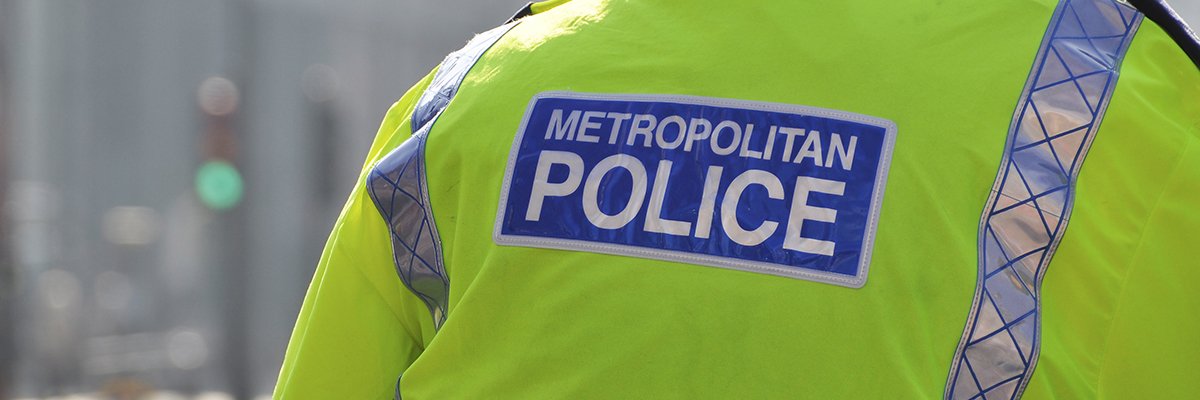
Just 30% of Metropolitan Police officers have completed the force’s mandatory data protection training, the London Assembly has reported, amid a slew of data incidents at the force.
The UK’s data regulator previously found serious flaws in the Met Police’s data protection training on 5 August 2026, when it issued the force with a formal enforcement notice and reprimand over breaches relating to the sharing of unredacted documents.
In one incident, an officer sent information that revealed a victim’s new contact details to their alleged stalker, while in another, an officer sent a bulk email that disclosed the identities of people linked to a high-profile criminal investigation where individuals associated with UK Parliament were targeted by someone attempting to gather compromising information.
While the Information Commissioner’s Office (ICO) disclosed at the time that the Met’s “training completion rates remain low”, the actual number was not revealed.
Following this, in mid-August 2026, the Met was forced to apologise for sharing the email addresses of people who claimed they were sexually abused by former Harrods owner Mohamed Al-Fayed, which it claimed occurred due to “human error”.
Now, following questioning from Green Party London Assembly member Benali Hamdache during a Police and Crime Committee meeting, the Met has revealed that only 30% of officers have completed their mandatory data protection training.
The revelation comes from Kenny Bowie, the force’s director of strategy and oversight, who told London Assembly members that while the low uptake “wasn’t particularly good” and the figure needs “to be improved”, it was ultimately the personal responsibility of individual officers and their leaders to ensure compliance.
He added that although an organisation of roughly 40,000 people dealing with hundreds of thousands of cases is never going to “entirely eradicate human error”, a three-pronged approach revolving around “personal responsibility, a supervisory responsibility, and a sort of technological layer on top of that” can help alleviate the issue.
On the technology layer, he suggested a system that could prompt officers when CC’ing non-Met officers and staff on e-mail chains.
However, while Bowie admitted that compliance must be achieved “as quickly as possible”, and further highlighted the potentially “corrosive impact” such breaches could have on victims coming forward, he declined to put a timeframe on when substantial compliance will be achieved.
“There is an imperative upon the Met Police to do this,” he said, adding that supervisors need to make the importance of data protection clear: “That needs to be driven down through the pyramid”.
Responding to the low data protection training figures, Hamdache said: “The Met have only just apologised for yet another serious data breach involving the personal information of the Al-Fayed victims. These are survivors who have already shown enormous courage in coming forward and who trusted the police with some of the most painful memories they have.
“We’re now learning that the force has been failing to meet basic standards in mandatory data protection training,” he added. “This is unacceptable and falls woefully short of the standards the public has every right to expect from its officers.
“Every officer must complete the mandatory data training as a matter of priority, and I will continue using my voice on the London Assembly to push for this.”
Ongoing data protection issues
There have been numerous previous instances where the ICO found the Met’s data protection practices to be lacking.
In November 2018, for example, an ICO investigation into the Met Police Gangs Matrix, an intelligence database used to identify and monitor individuals considered to be linked to gangs, found serious breaches of data protection laws in the force’s use of the tool.
This included the complete absence of an Equality Impact Assessment, a lack of central oversight or governance over the processing of the data, and the blanket sharing of sensitive personal data with third parties despite the absence of any information-sharing agreements.
The Gangs Matrix tool was eventually scrapped in February 2024, although human rights groups have continued to express concerns about a potential replacement system repeating the same mistakes.
In December 2020, the Met also failed to comply fully with an ICO enforcement notice regarding its backlog of 662 subject access requests, which noted the force had “sustained failures” in dealing with people seeking to identify what personal information the force holds on them.
The ICO said at the time that while “it is also clear that the situation is not yet fully resolved”, the commissioner had decided there would be “no need for further regulatory action”.
In August 2023, Computer Weekly reported that the Met also deployed an integrated record management system called Connect in November 2022, despite data protection “compliance issues” that would inhibit its ability to retrieve data, meet its statutory logging requirements and respond to subject access requests.
A serving Metropolitan Police officer was dismissed in November 2024 after repeatedly accessing sensitive files related to the disappearance and murder of Sarah Everard while off-duty, prompting concern that legal requirements around police data access were not being followed.

